Afternoon edition··Coverage: since morning (~08:00 Berlin / ~5h)
What matters
Plugin4Shell: zero-click RCE hits Claude Code/Codex/Copilot/Gemini CLI; Gmail AI Overviews for Workspace; Xi–Trump summit framed as trade-truce extension.
AIR Security discloses Plugin4Shell: a zero-click RCE that defeats plugin SHA pinning in Claude Code, OpenAI Codex, GitHub Copilot, and Gemini CLI — dubbed the first supply-chain flaw of the AI-agent ecosystem.
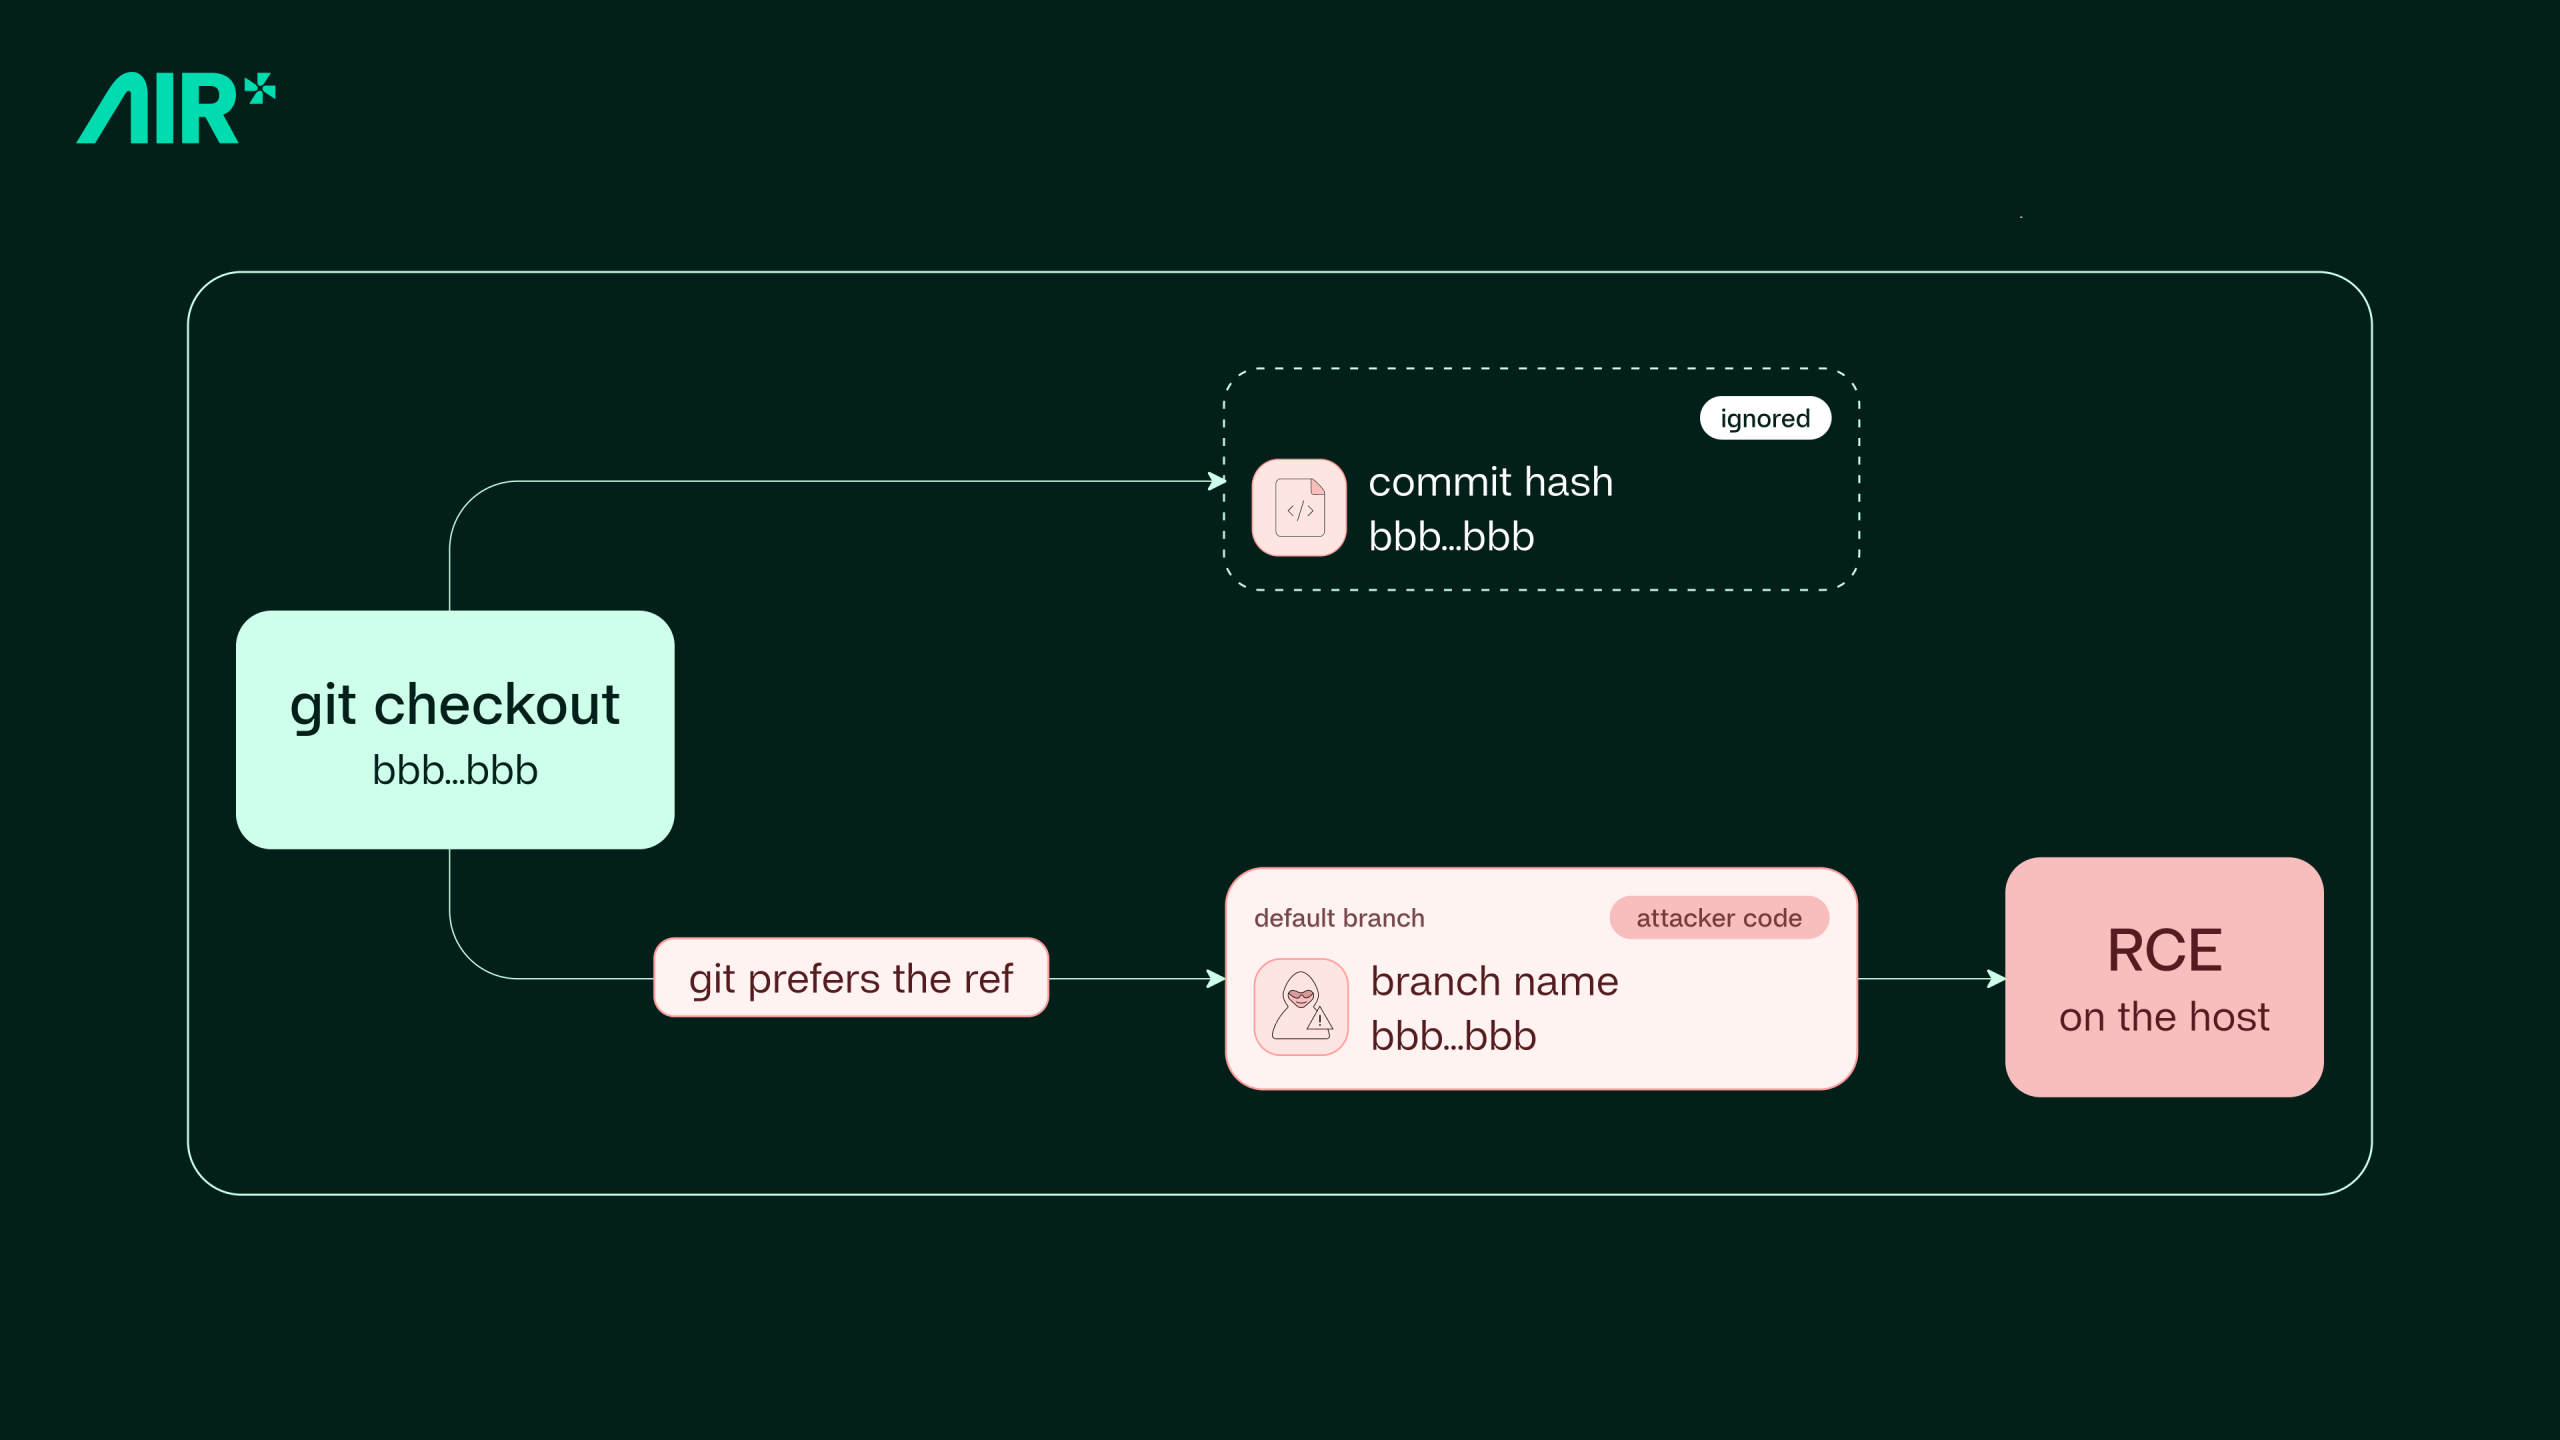
Attack: agent checks out the pin but never verifies working-tree HEAD; attacker names a branch after the 40-char hash (or Gemini FETCH_HEAD trick) so git prefers malicious code while the pin still “looks” honored.
Zero-click trigger: Claude Code and Codex auto-update plugins in the background by default — a previously reviewed plugin can flip to attacker code with no install prompt.
Why it matters —Trusted marketplace plugins were supposed to be pinned-safe; this class of bug hands an attacker the agent host — source, keys, CI — unless every vendor ships a post-checkout HEAD check.
heise: Google is rolling AI Overviews into Gmail search for paying Workspace customers worldwide — natural-language Q&A over the mailbox instead of hit lists (e.g. open invoices, trip details).
Rapid Release domains since ~Sep 3; Scheduled Release full rollout starts Sep 21. Gmail UI must be set to English; admins need Gemini for Workspace + Workspace Intelligence on Gmail.
Why it matters —Mailbox search becomes an answer engine for paid Workspace — while EU consumer Gmail stays out, widening the enterprise/consumer AI feature split.
heise: SolarWinds ARM CVE-2026-28326 (high) — remote unauth attackers can push code via a hardcoded static key, risking full compromise of the rights-management host.
Fixed in ARM 2026.2.1 (also Exchange Online mailbox-rights display bugs). No evidence of active exploitation yet, per vendor/heise.
Why it matters —A rights-management appliance with unauth RCE is a high-value jump box — patch or upgrade off EoL before someone chains it into domain-wide access.
CNA/Reuters wire: Trump–Xi Washington meeting set for Sep 24; analysts say Xi has little urgency for concessions after China’s export surge, while Trump faces weak approval and a costly Iran war.
Main ask: signal extending last year’s trade truce that averted a bigger shock; China’s global surplus is on pace to top $1T for a second year (“China Shock 2.0”).
Why it matters —Afternoon framing for Thursday’s summit: expect truce-extension signaling more than a grand bargain, with AI/trade side-channels and Taiwan as the quiet pressure point.
BVB: after 1:0 at Stuttgart, club notes perfect start across BL/Pokal/CL; Ricken “Stresstest bestanden!”; Kovac avg 2.17 pts/game (club-best vs Tuchel/Favre/…); next home Werder Oct 9 after Länderspielpause (bvb.de).bvb.de
ESA + ISRO extend Cooperative Agreement five years to Jan 8 2032; scope adds space weather + human/robotic exploration (signed Paris, International Space Summit margins Sep 10; posted today).ESA